Lumina — Zero-Knowledge Ephemeral Secrets & Secure Transfer Platform
Live Production Application: lumina.nordcode.site
Core Promise: Zero-knowledge, client-side encrypted ephemeral secret delivery without accounts, server-side data retention, or plain-text exposure.
1. Overview & Platform Architecture
OpenPGPIn-browser client-side E2EE encryption
0 BytesServer-side plaintext knowledge or residue
< 1msCompiled Go stateless engine response time
100%Instant purge upon first retrieval or TTL
2. Secret Creation & Zero-Knowledge Cryptographic Core
Key Cryptographic Foundations:
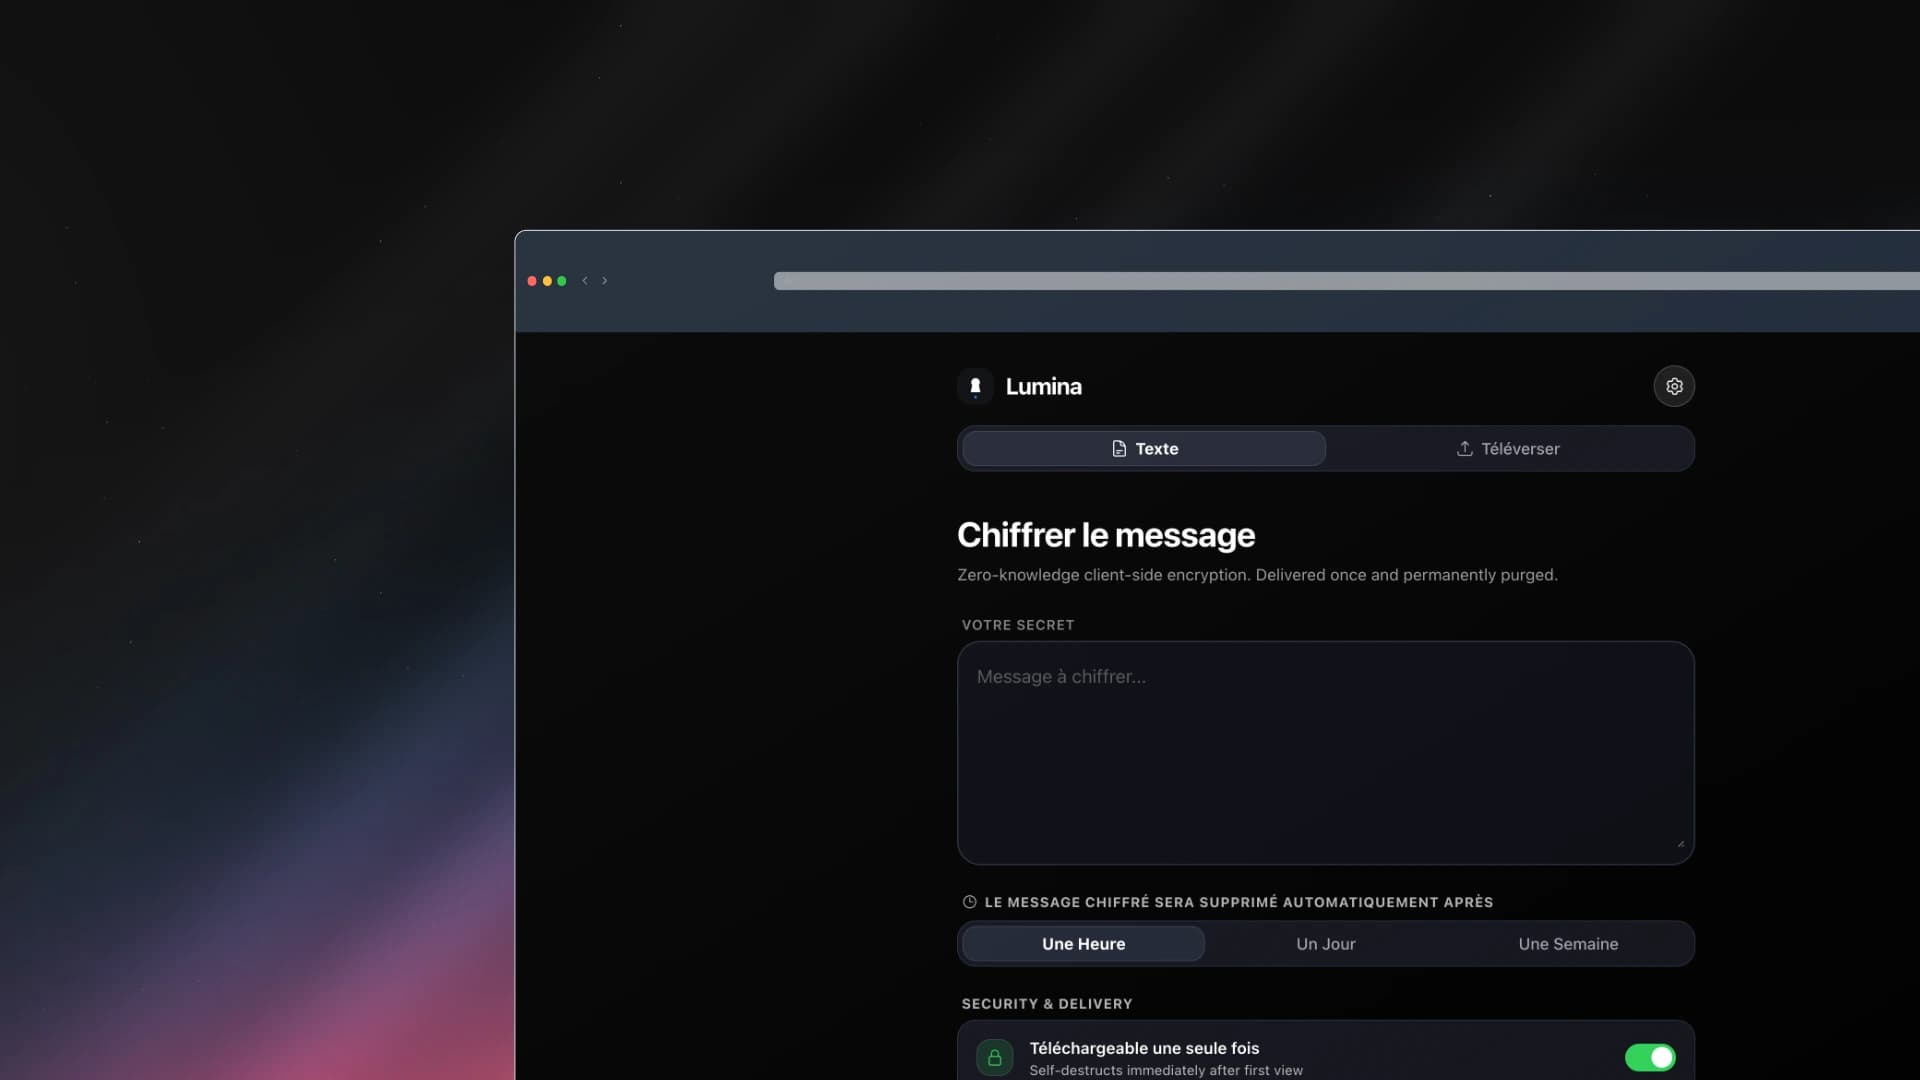
- In-Browser Encryption: All payloads (text, passwords, credentials, configuration files) are encrypted directly in the user's browser using OpenPGP prior to network transit.
- Zero-Trust Server Boundary: The backend server receives and stores only encrypted ciphertext. It never receives or stores plaintext data, private keys, or decryption passphrases.
- Fragment-Based Key Delivery: The cryptographic decryption key is embedded solely in the URL hash fragment (#key). Because browsers do not transmit URL fragments to HTTP servers, the key never touches server access logs, reverse proxies, or transit networks.
- Argon2id Key Derivation: Optional custom passphrases are hardened using the memory-hard Argon2id key derivation function, neutralizing GPU/ASIC dictionary attacks.
3. Cryptographic Link Generation & Distribution
Generation & Sharing Features:
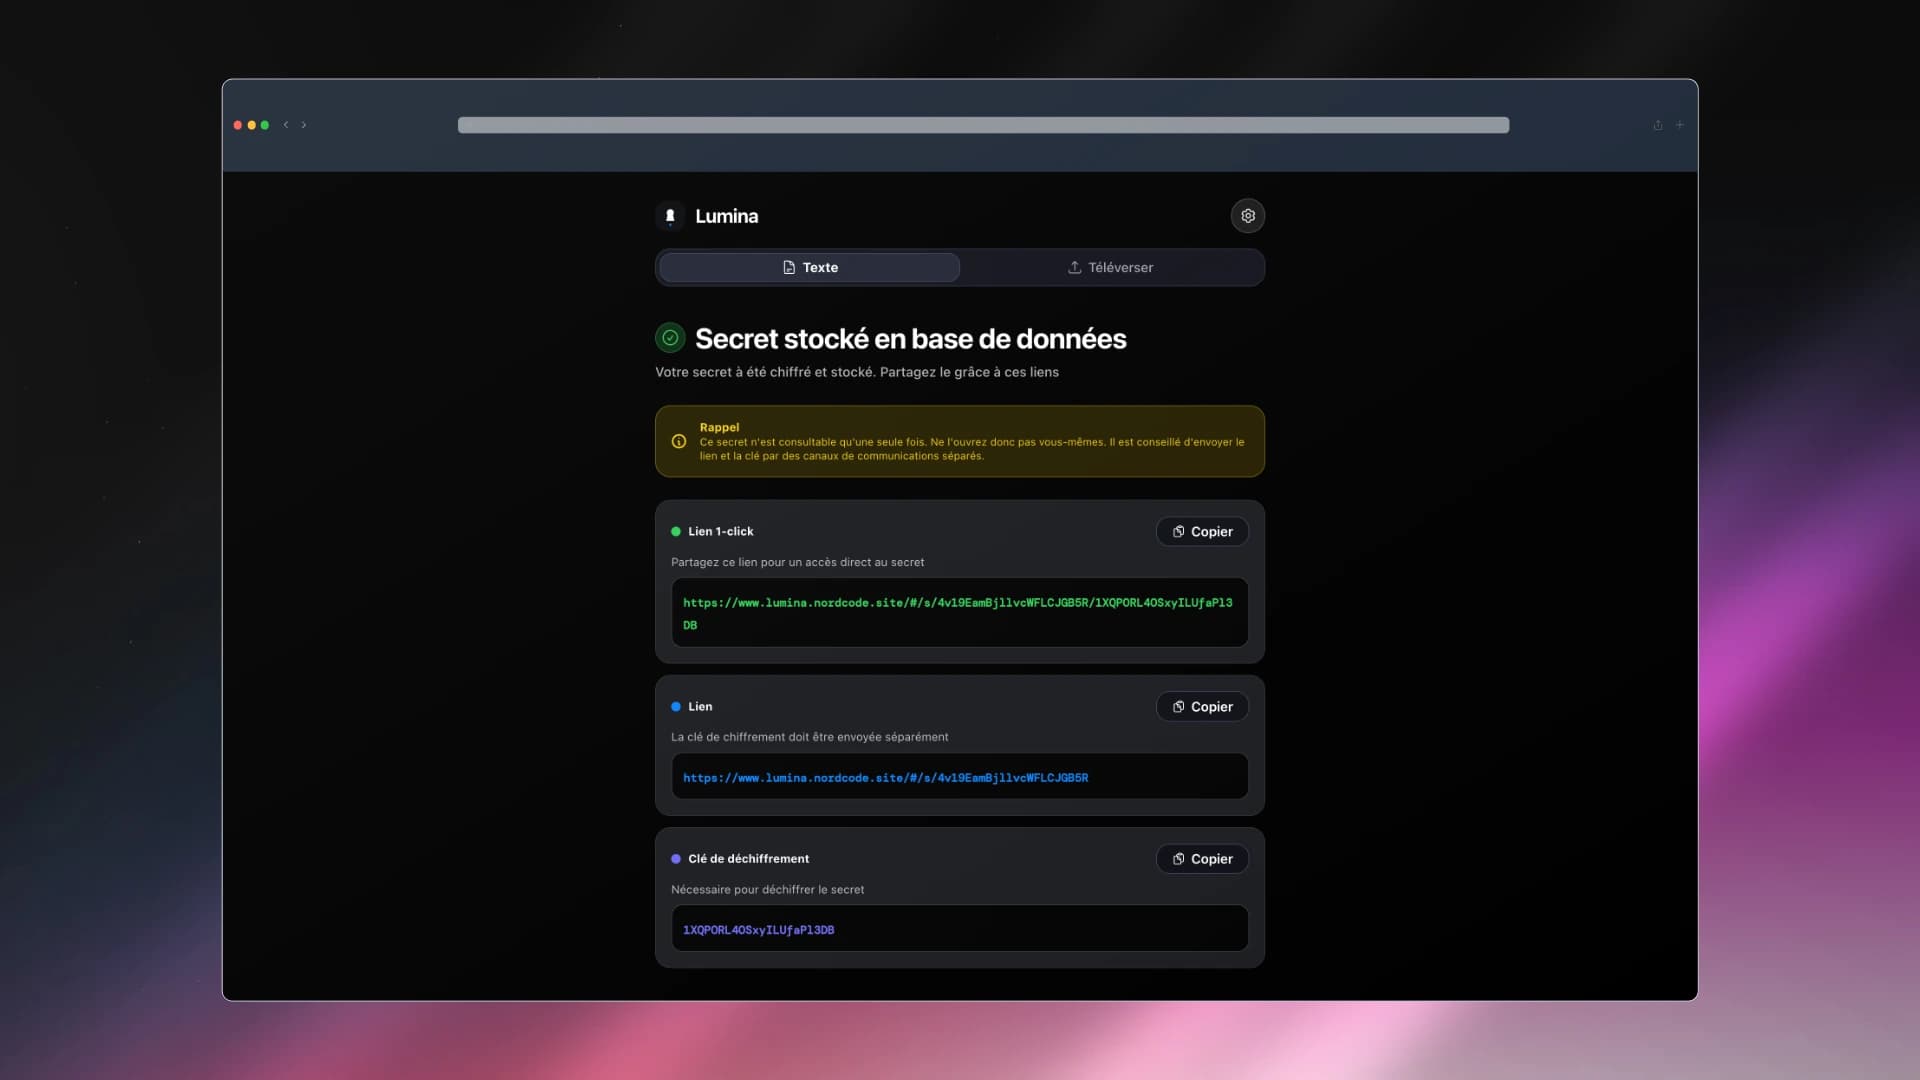
- One-Click Clipboard Copying: Instant tactile copy confirmation with visual dynamic HUD feedback.
- Integrated QR Code Generation: Generates high-contrast QR codes for secure, air-gapped mobile handoffs.
- Volatile Storage Registration: Ephemeral registration into ultra-fast in-memory storage (Memcached or Redis) with strict automated TTL eviction.
4. Recipient Experience & Decryption Safeguards
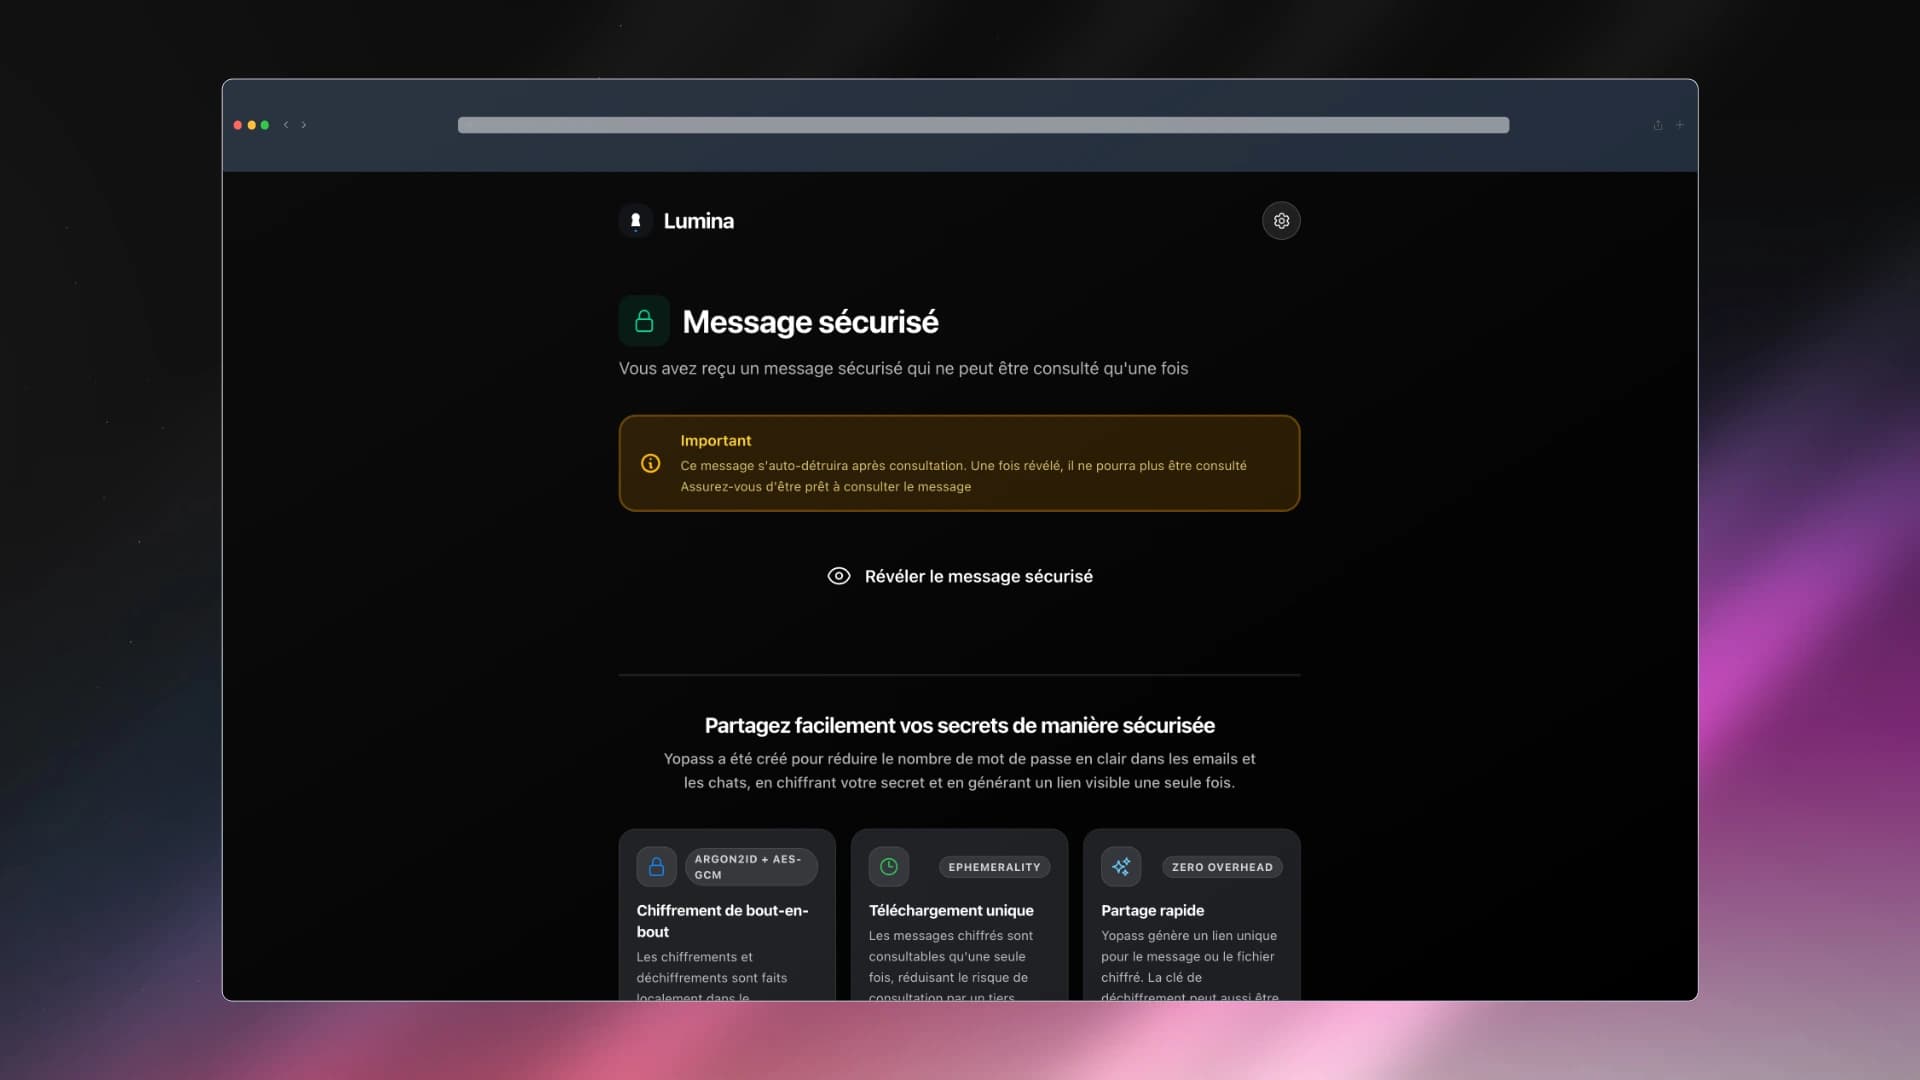
Passphrase Verification & Decryption:
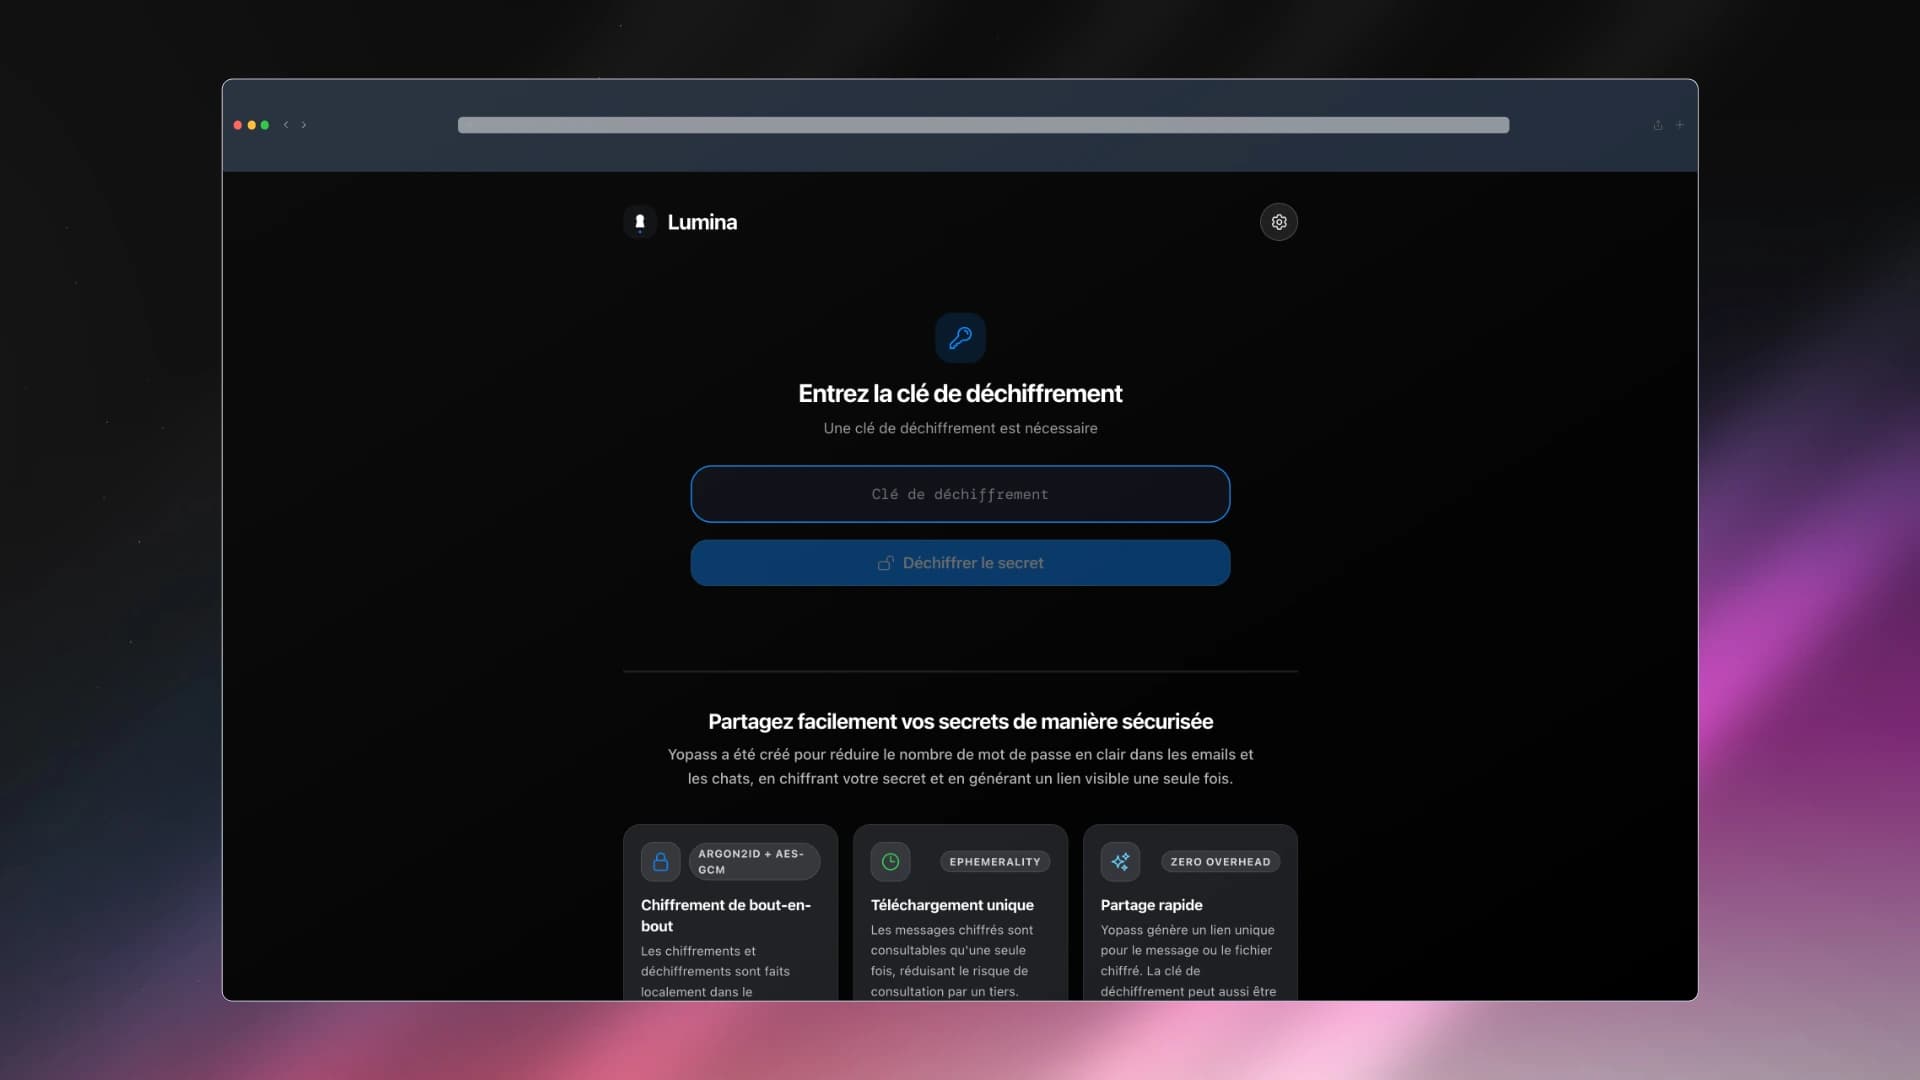
- Dual-Layer Protection: Link interceptors cannot decrypt payloads without the out-of-band passphrase.
- Instant Purge Trigger: The backend immediately burns the ciphertext from volatile storage upon retrieval, ensuring single-use delivery.
5. Decrypted View & Ephemeral Destruction
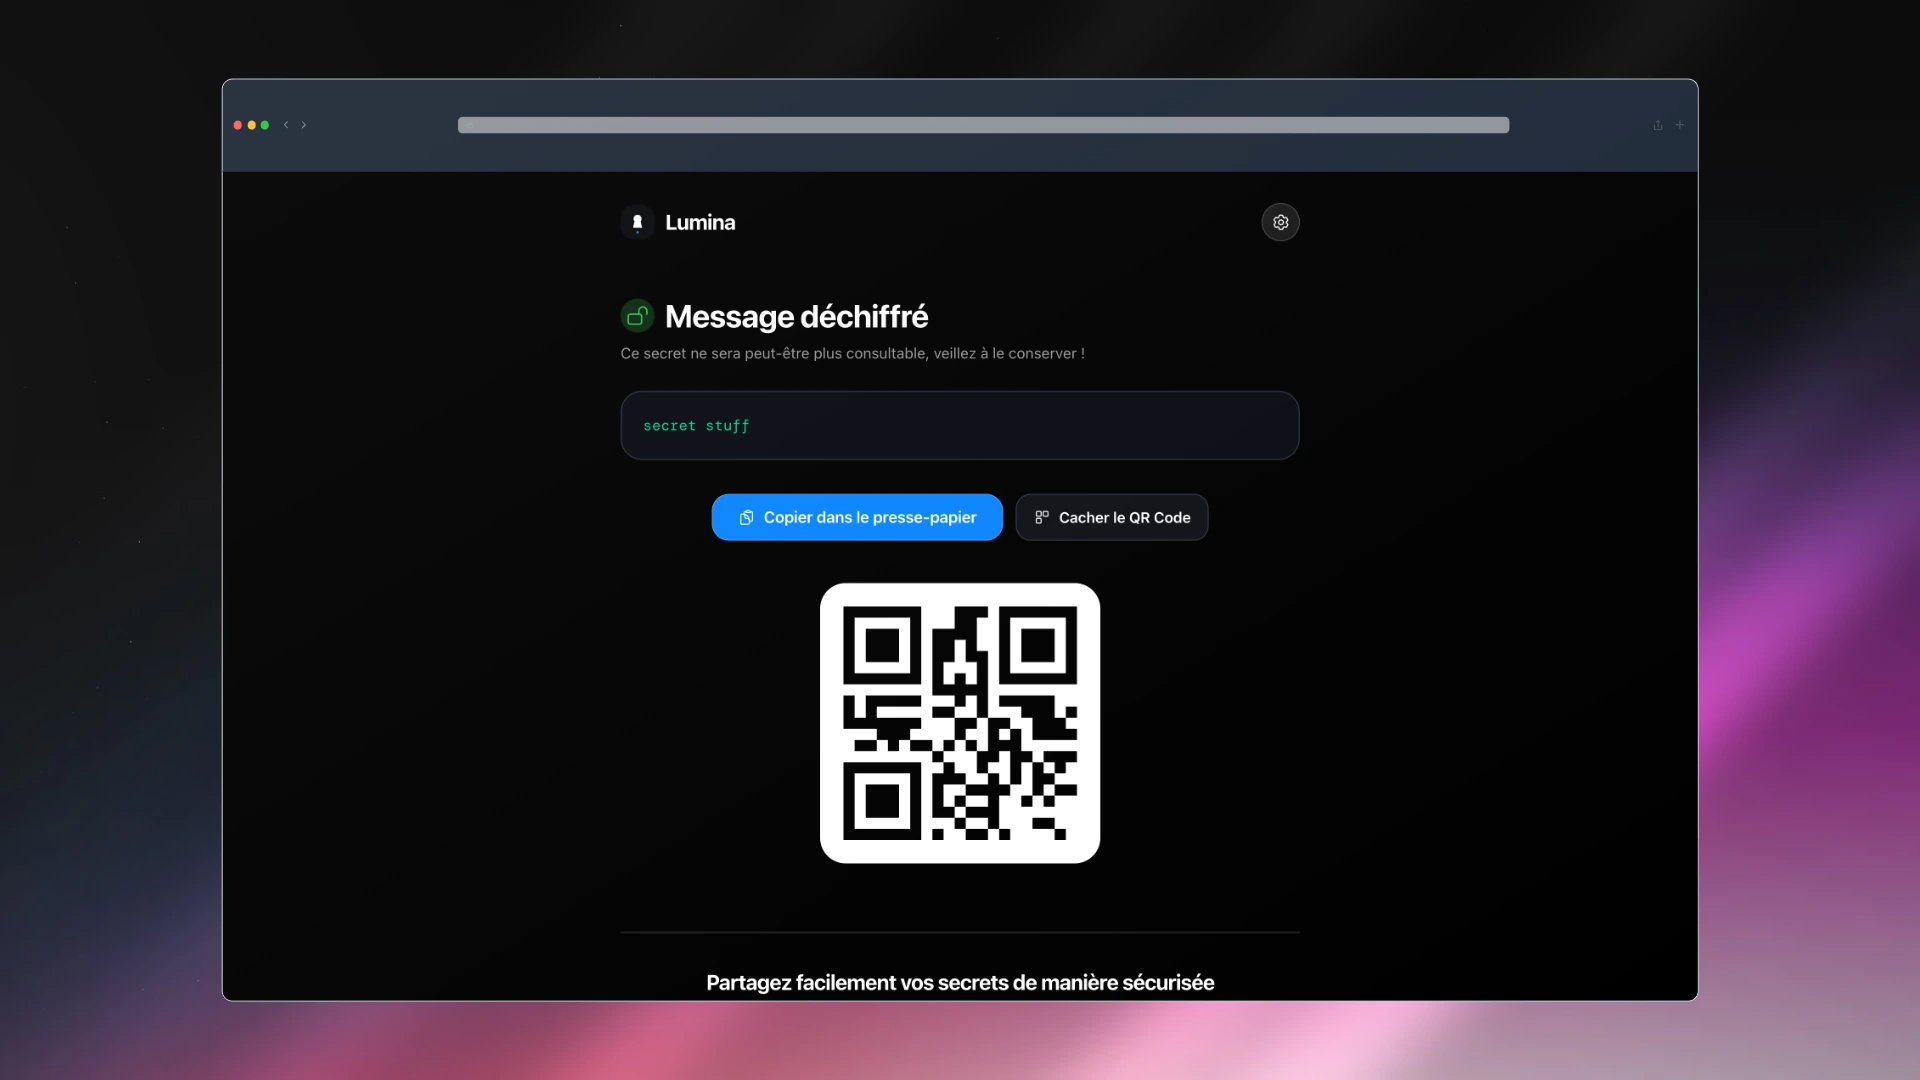
- Monospace Syntax Preservation: Preserves exact whitespace, indentations, line endings, and character encodings for .env files, SSH private keys, and JSON payloads.
- Self-Destruction Confirmation: Clear visual confirmation that the secret has been permanently purged from server memory and cannot be re-opened.
6. Content, File Streaming & Reverse Requests
Streaming Large File Encryption
- Direct Client-Side Chunking: Files are chunked and encrypted on-the-fly in browser memory prior to transmission.
- Low Memory Overhead: Streaming architecture enables uploading and downloading multi-megabyte binary assets without exhausting client or server RAM.
- End-to-End File Integrity: Files remain fully encrypted at rest on storage backends (Local Disk or S3/MinIO) until decrypted in the recipient's browser.
Secret Requests (Inverted Sharing Workflow)
- Secure Retrieval from Non-Users: Allows teams to request credentials or sensitive files from external clients, third-party vendors, or contractors without requiring account creation.
- One-Time Submission Portals: Each request link generates a dedicated upload portal restricted to a single submission.
- Client-Side Recipient Public Key Encryption: When a vendor submits the form, data is encrypted directly with the requester's ephemeral public key before transmission.
7. Tracking, Verification & Enterprise Governance
Real-Time Read Receipts
- Decryption Confirmations: Senders can opt-in to receive cryptographic read receipts confirming the exact moment their secret was opened and decrypted.
- Eliminates Delivery Ambiguity: Eliminates guesswork regarding whether a client or teammate received critical credentials.
Enterprise Webhooks & Audit Logging
- Signed Lifecycle Events: Sends cryptographically signed (HMAC-SHA256) webhooks on key lifecycle triggers (Created, Decrypted, Expired, Burned) for automated SIEM / Slack integration.
- Structured NDJSON Output: Generates machine-readable, append-only audit event streams formatted to satisfy SOC 2 Type II, ISO 27001, GDPR, and HIPAA compliance frameworks without leaking plaintext or keys.
- OIDC / SSO & Domain Restrictions: Integrates with Okta, Microsoft Entra ID / Azure AD, and Google Workspace to enforce corporate domain authentication for secret creation.
8. Architecture, Deployment & Infrastructure
Storage Engine Flexibility
- In-Memory Cache (Memcached): Volatile, ultra-fast storage where records naturally evict upon expiration or restart.
- Persistent Distributed Cache (Redis): Redis cluster support for multi-instance replication, high availability, and persistent queueing.
- Hybrid Storage Backends: Decoupled metadata and blob storage, enabling encrypted file payloads to reside on Local POSIX Filesystems or S3-Compatible Object Storage (AWS S3, MinIO, Cloudflare R2).
Split-Instance & Read-Only Topology
- Isolated Network Segmentation: Support for split-node deployments where write/creation nodes run in private subnets behind corporate VPN/SSO, while lightweight read-only instances face the public internet to serve recipients.
- Prometheus Metrics & Health Probes: Native /metrics, /healthz, and /livez endpoints for Kubernetes cluster orchestration and real-time observability.
9. Lumina Fluid Interface & Apple Design System
Apple Human Interface & Fluid Motion
- Cardless Canvas Architecture: Elimination of boxed card boundaries in favor of a unified, distraction-free spatial canvas.
- Refined Material Aesthetics: Translucent glass layers (backdrop-filter: blur(28px)), hairline light-catching borders, and Apple system color tokens.
- Adaptive Dark & Light Modes: Obsidian Space-Black (#000000) for OLED displays and clean Porcelain Ceramic Light (#ffffff / #f5f5f7).
- Critically Damped Physics: Custom spring curves (damping: 1.0, response 0.35s) for smooth, non-distracting visual state transitions.